Authentication in ReCaS Bari
All services provided by the data center, as well as the forms used to request and manage accounts, use a centralized authentication system based on Single Sign-On (SSO).
When a service requires authentication, users are redirected to the following page (temporary image):
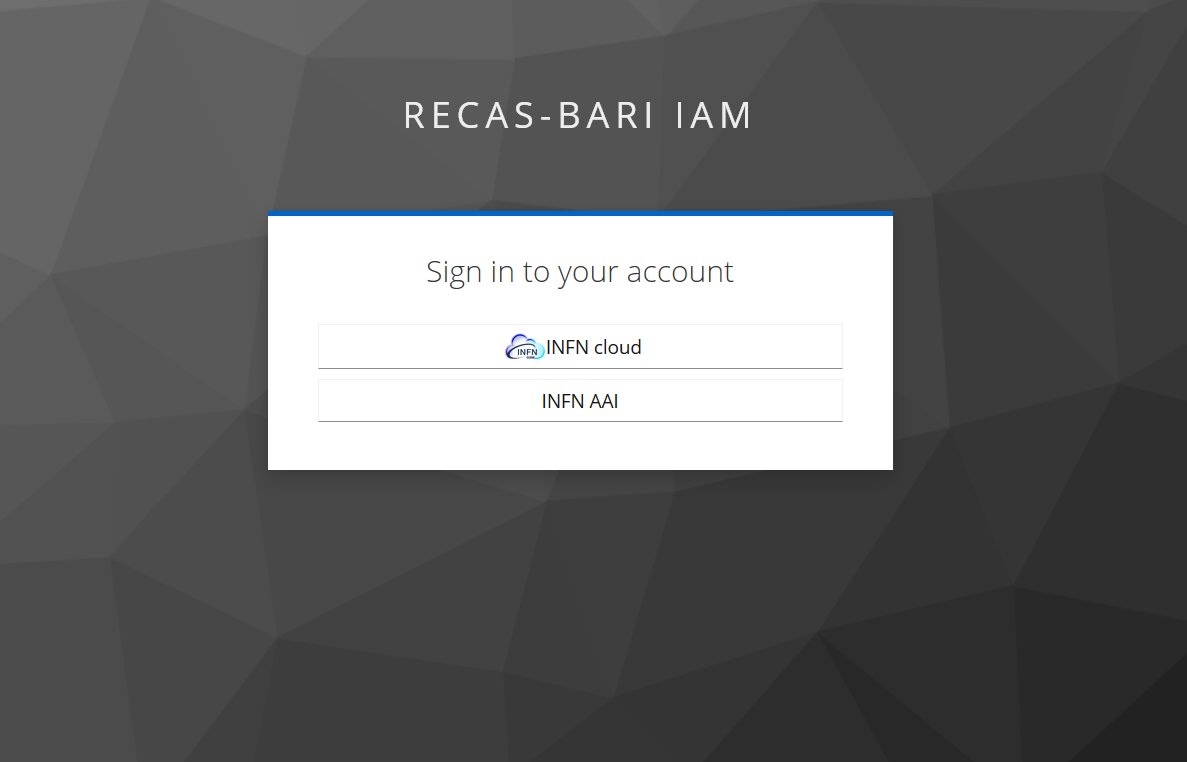
From this interface, users can authenticate with their organization's credentials by selecting its Identity Provider (IdP). Dedicated buttons are available for the Italian National Institute for Nuclear Physics (INFN) and the University of Bari Aldo Moro (UniBa), alongside the IDEM/eduGAIN option for access through the IdPs of federated organizations.
The ReCaS Bari data center is jointly managed by INFN and UniBa. Users from these two institutions can authenticate by selecting their institution's button.
Users from other research organizations, universities, or institutions can authenticate through the IDEM/eduGAIN option, provided that their home organization participates in one of the supported identity federations. This option allows users to select their organization's IdP from those of federated institutions at national and international levels.
Local ReCaS Account
Only if authentication through all available Identity Providers is not possible, a local account on an IdP managed by the ReCaS staff may be requested.
This option should be considered residual and requires a rigorous user identification process. It also involves the collection, retention, and processing of personal data needed for identification, according to procedures that differ from those used by federated Identity Providers and are indicated at the bottom of this page.
Support
In case of problems or questions, users can contact user support through the dedicated support request form.
Personal Data Processing
For information on personal data processing, see the dedicated section.